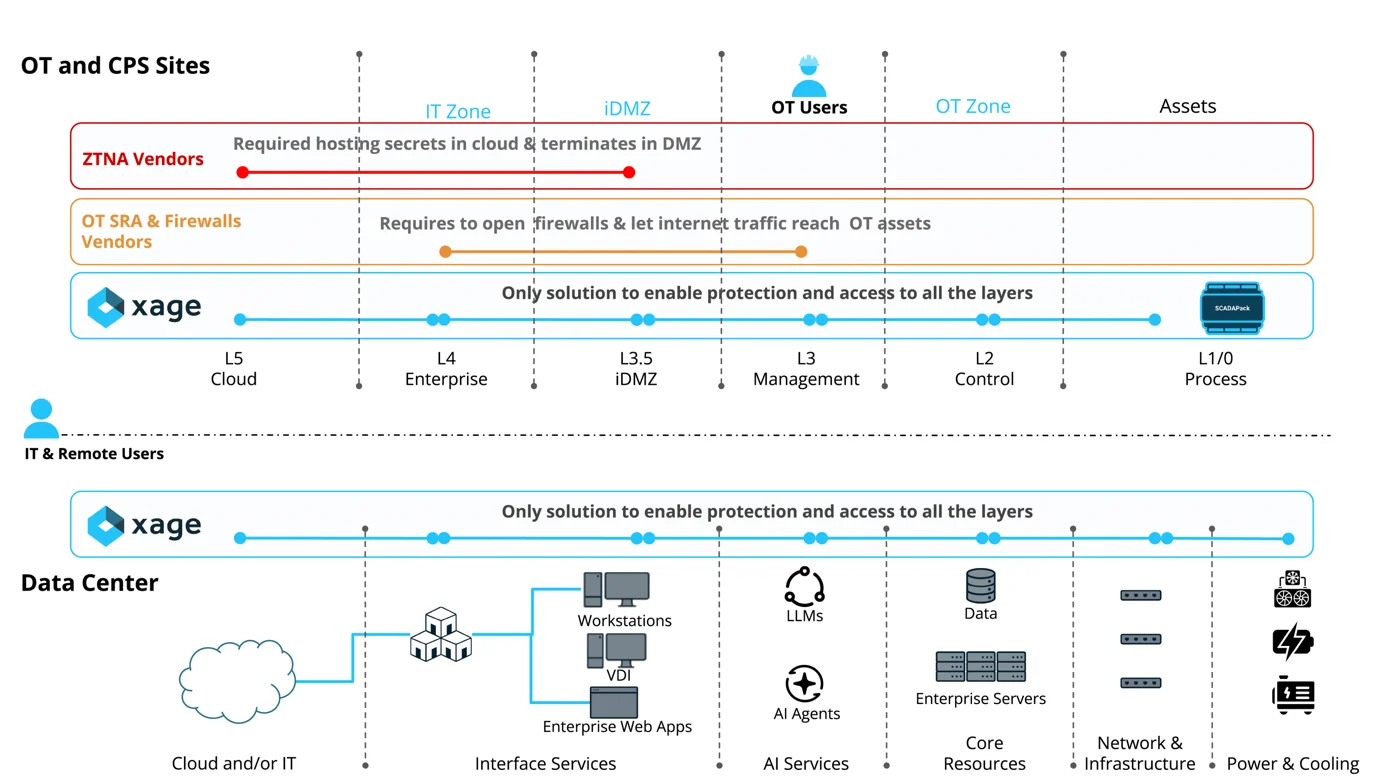
Xage Secure Remote Access ↗
Plan controlled access to operational and business systems.
Review product requirements ↗
Zero trust identity and access for IT and operational environments. Discuss selection, integration and support requirements with MMC UAE for your Dubai, Abu Dhabi or wider UAE project.
Review individual offerings, then send your requirements for edition, compatibility and service planning.
Plan controlled access to operational and business systems.
Review product requirements ↗
Review privileged identity and access approval requirements.
Review product requirements ↗
Plan the platform architecture for distributed access controls.
Review product requirements ↗
Review trusted exchange of information between environments.
Review product requirements ↗Xage’s portfolio separates secure remote access, privileged access, platform architecture and controlled data exchange. Remote access concerns a route to particular assets. Privileged access concerns elevated authority and its custody. Fabric is an architecture-level discussion across distributed controls. Data Exchange concerns authorised information flows, which should not automatically grant a user broad network reach.
Start with employees, vendors, service identities and the assets they need. Operational environments also require a distinction between permission to connect and permission to change equipment. A vendor session may be technically available while a maintenance action still needs plant approval. Record those decisions before discussing automation or a unified control plane.
Confirm target protocols, identity integration and supported component versions. A pilot should follow a real maintenance task from request through approval, connection and closure, including denial and expiry. Privileged credential changes need dependency checks. Data exchange needs a defined producer, recipient, protocol and failure behaviour.
For distributed UAE installations, review communications loss, local operating needs and the recovery path when central identity services are unavailable. Do not assume identical connectivity at every site. Handover should include the component map, policy owners, emergency procedure and evidence-review responsibilities. Product licensing, manufacturer support and any MMC implementation or ongoing service should be stated separately so the platform name does not become an unsupported service-level promise.
Useful answers to help you plan your next step.
Discuss your requirements ↗No. The asset owner’s maintenance and change permissions remain a separate part of the operating procedure.
Contact our team about products, installation or ongoing support.
14th Floor, Tamani Arts Building, Business Bay, Dubai
Xage Security