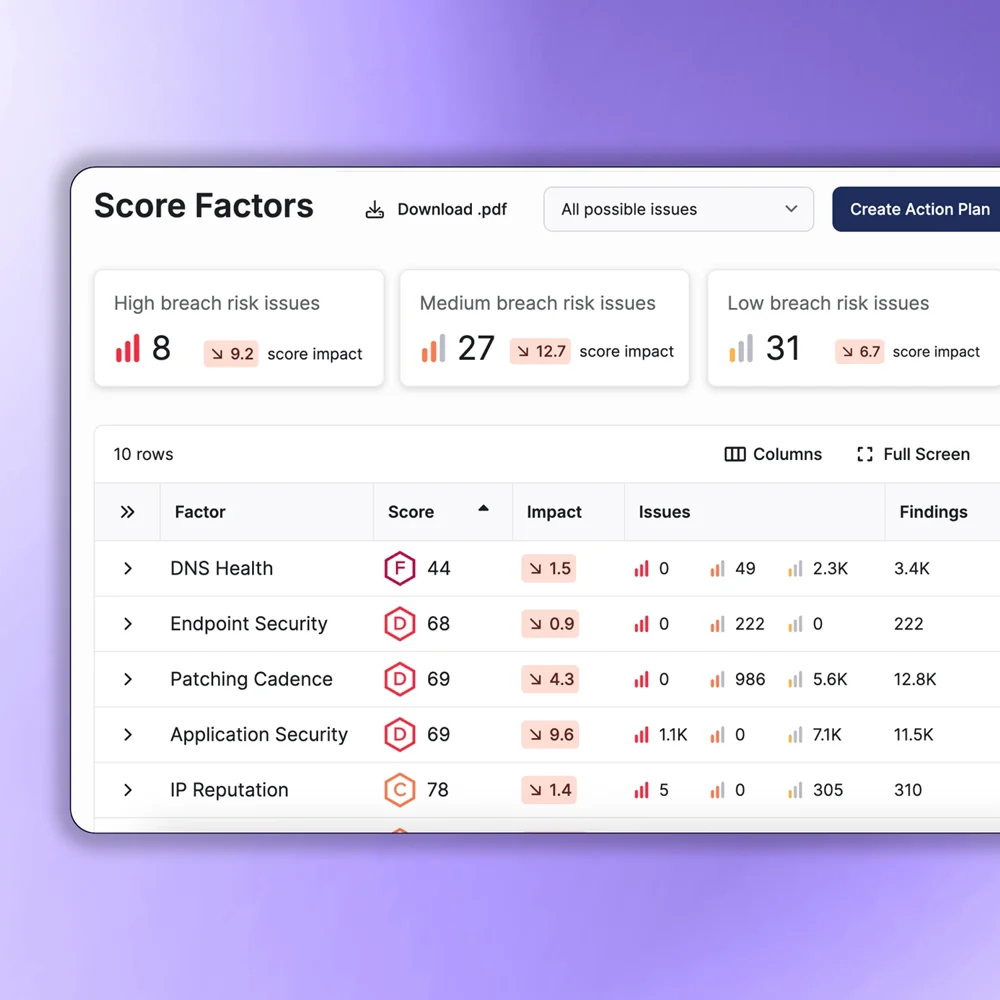
SecurityScorecard Security Ratings ↗
Review external ratings for your organization and suppliers.
Review product requirements ↗
External security ratings and third-party risk visibility. Discuss selection, integration and support requirements with MMC UAE for your Dubai, Abu Dhabi or wider UAE project.
Review individual offerings, then send your requirements for edition, compatibility and service planning.
Review external ratings for your organization and suppliers.
Review product requirements ↗
Plan questionnaire exchange and third-party review.
Review product requirements ↗
Review external asset intelligence for investigation.
Review product requirements ↗
Plan business impact modeling with documented assumptions.
Review product requirements ↗SecurityScorecard’s catalogue includes Security Ratings, Security Assessments, Attack Surface Intelligence and Cyber Risk Quantification enquiries. External observations, questionnaires, asset discovery and business-impact models answer different questions. The first decision is which supplier or organisational relationship is being assessed and why its service matters.
A rating is one input, not a complete determination that a supplier is secure or unsuitable. Asset attribution can be wrong, questionnaires need evidence and quantified estimates depend on assumptions. Record the service provided, access granted and consequence of failure so external data is interpreted in the right business context. Confirm current product packaging rather than assuming every capability is part of a ratings licence.
Pilot known organisations and review representative observations with authorised owners. Test attribution correction and the route for explaining a disputed result. For assessments, define evidence requests, review and sign-off. For quantification, retain scenario inputs, uncertainty and the decision the estimate supports.
UAE customers should determine applicable procurement and sector requirements through their authorised teams, not infer compliance from a score. Handover needs supplier ownership, review cadence, exceptions and remediation tracking. External contacts or disclosure of internal findings require the organisation’s approval. Reporting should show evidence, context and changes over time, with a practical response when the platform identifies something the service owner cannot immediately resolve.
Useful answers to help you plan your next step.
Discuss your requirements ↗No. Combine relevant external signals with service context, contractual requirements and reviewed evidence.
Contact our team about products, installation or ongoing support.
14th Floor, Tamani Arts Building, Business Bay, Dubai
SecurityScorecard