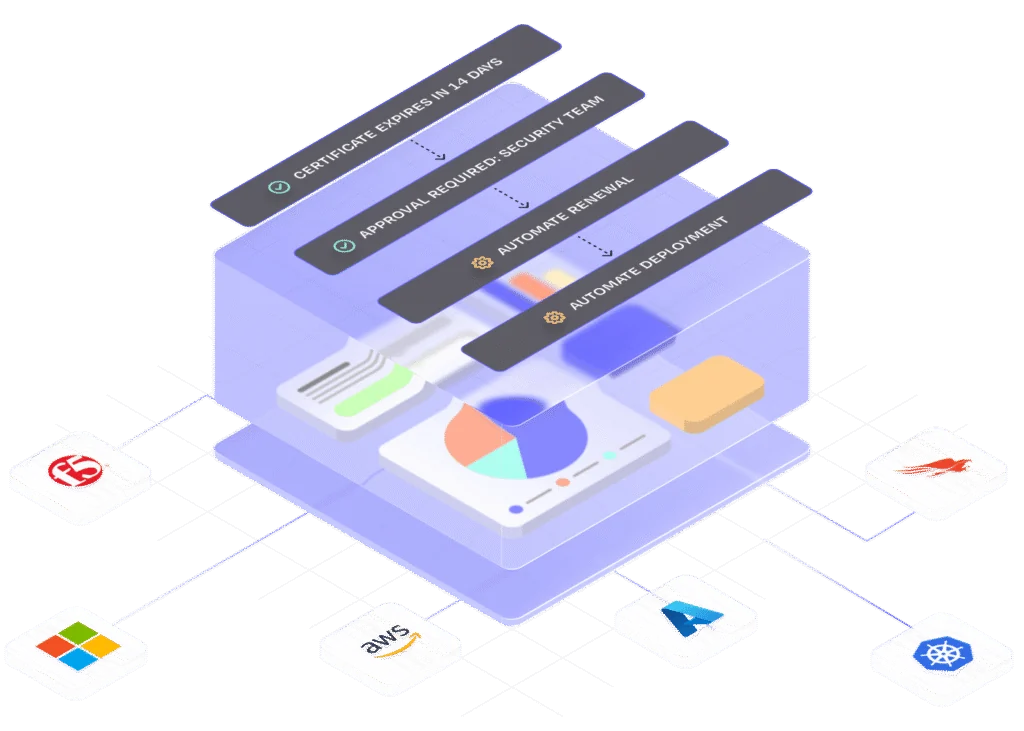
Keyfactor Certificate Lifecycle Automation ↗
Plan discovery and renewal workflows for enterprise certificates.
Review product requirements ↗
Digital trust, certificate automation and public key infrastructure. Discuss selection, integration and support requirements with MMC UAE for your Dubai, Abu Dhabi or wider UAE project.
Review individual offerings, then send your requirements for edition, compatibility and service planning.
Plan discovery and renewal workflows for enterprise certificates.
Review product requirements ↗
Review certificate issuance for devices, workloads and applications.
Review product requirements ↗
Plan approval and signing workflows for software delivery.
Review product requirements ↗Keyfactor’s portfolio separates three related decisions. Certificate Lifecycle Automation concerns discovery, renewal and deployment of certificates already used by services. Modern Private PKI concerns issuing and trusting identities for devices, workloads and applications. Secure Code Signing concerns controlled signatures on released software artefacts. An organisation may need more than one, but a certificate inventory problem should not automatically become a replacement of its issuing authorities.
Start by identifying the failure you need to prevent: unknown certificates, manual installation, inconsistent enrolment or insufficient control of signing keys. That distinction determines the first pilot and the system owners who must participate. Application teams, PKI administrators and release engineers have different responsibilities, even where they share the same cryptographic foundation.
A useful evaluation follows an identity from request to its successful use. For renewal, demonstrate installation and service validation after issuance. For private PKI, validate enrolment, trust and revocation on an actual supported endpoint. For signing, verify the released artefact on its consuming platform and check approval of the signing request.
The proposal should identify supported issuers, endpoint integrations, key-custody arrangements and recovery responsibilities. Define which tasks remain manual. For a business operating several UAE sites, administrator reachability and ownership across business units can limit automation even when certificate issuance is centralised. Handover needs an actionable owner register and exception process, so a failed integration does not become an unnoticed expiry risk.
Useful answers to help you plan your next step.
Discuss your requirements ↗Not necessarily. Compare supported issuer connections with the requirement. Issuance architecture and lifecycle orchestration are separate design decisions.
Contact our team about products, installation or ongoing support.
14th Floor, Tamani Arts Building, Business Bay, Dubai
Keyfactor