Invicti DAST ↗
Plan scanning of running web applications and APIs.
Review product requirements ↗
Application security testing and risk prioritization. Discuss selection, integration and support requirements with MMC UAE for your Dubai, Abu Dhabi or wider UAE project.
Review individual offerings, then send your requirements for edition, compatibility and service planning.
Plan scanning of running web applications and APIs.
Review product requirements ↗
Review source-code security testing requirements.
Review product requirements ↗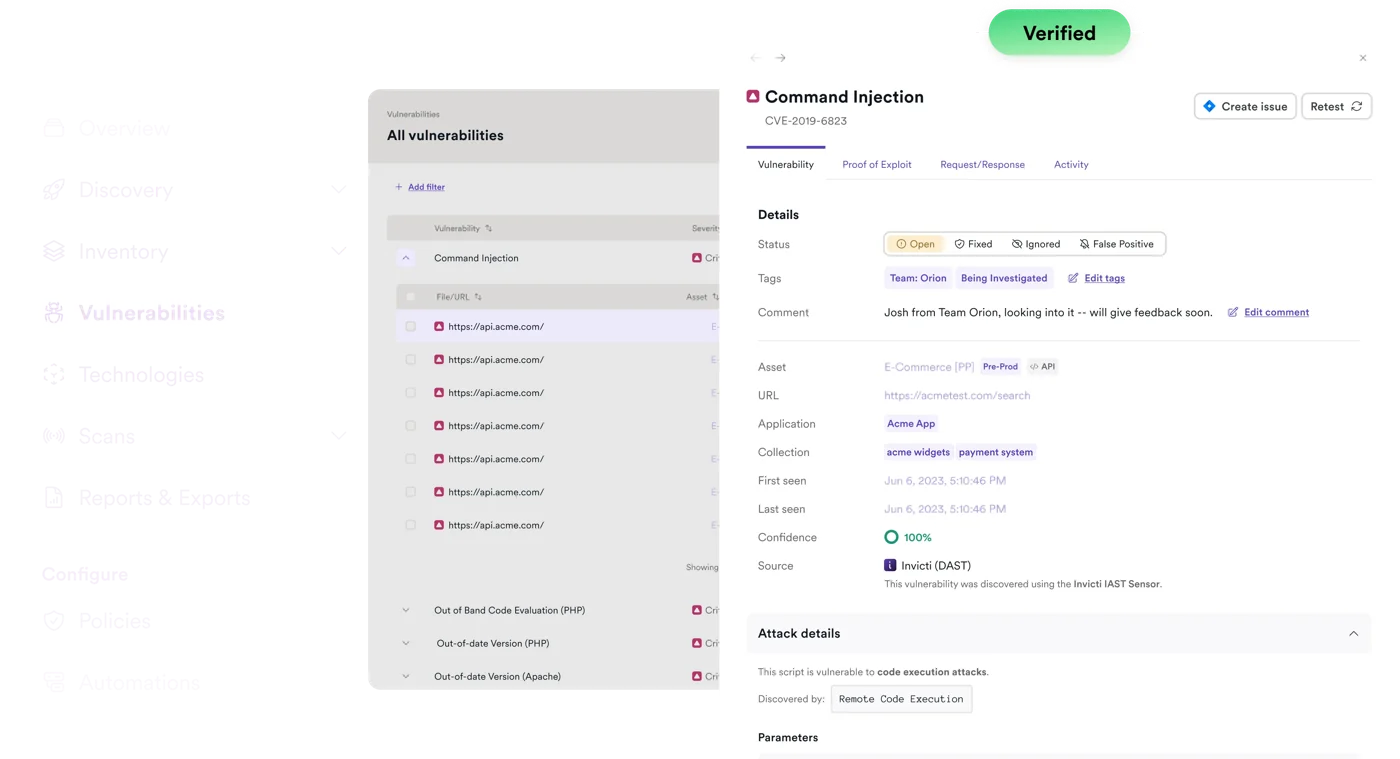
Plan assessment of application dependencies and component risk.
Review product requirements ↗Invicti’s catalogue separates DAST, SAST and SCA. DAST evaluates a running application within its authorised access and paths. SAST evaluates supported source or build representations. SCA concerns third-party components and their context. These methods complement one another, but a result from one should not be presented as evidence that the others are unnecessary.
Begin with application ownership, languages, authentication and dependencies. A public-page scan may miss authenticated workflows. Static coverage depends on supported technologies and configuration. A dependency finding needs version and applicability review. The objective is a remediable, attributable result rather than the largest possible count of alerts.
Select one representative application and agree written scope. Confirm credentials, safe test windows, exclusions and data handling for dynamic testing. For source and component assessment, use narrowly approved repository or artefact access. Trace a known issue into the team’s backlog and verify a correction through the appropriate retest.
Production activity needs stop conditions and the approval of relevant application owners; linked third-party systems do not automatically become authorised targets. UAE customers should confirm processing and access requirements before code or application data is shared. Handover should retain the coverage matrix, triage rules, exceptions and release decisions. This makes the testing programme usable as applications change instead of leaving an unattended scanner with unexplained gaps.
Useful answers to help you plan your next step.
Discuss your requirements ↗No. Record the access, paths and methods actually assessed, then identify remaining coverage and other required reviews.
Contact our team about products, installation or ongoing support.
14th Floor, Tamani Arts Building, Business Bay, Dubai
Invicti