Checkmarx SAST ↗
Plan source-code security analysis in development.
Review product requirements ↗
Developer-focused application security testing. Discuss selection, integration and support requirements with MMC UAE for your Dubai, Abu Dhabi or wider UAE project.
Review individual offerings, then send your requirements for edition, compatibility and service planning.
Plan source-code security analysis in development.
Review product requirements ↗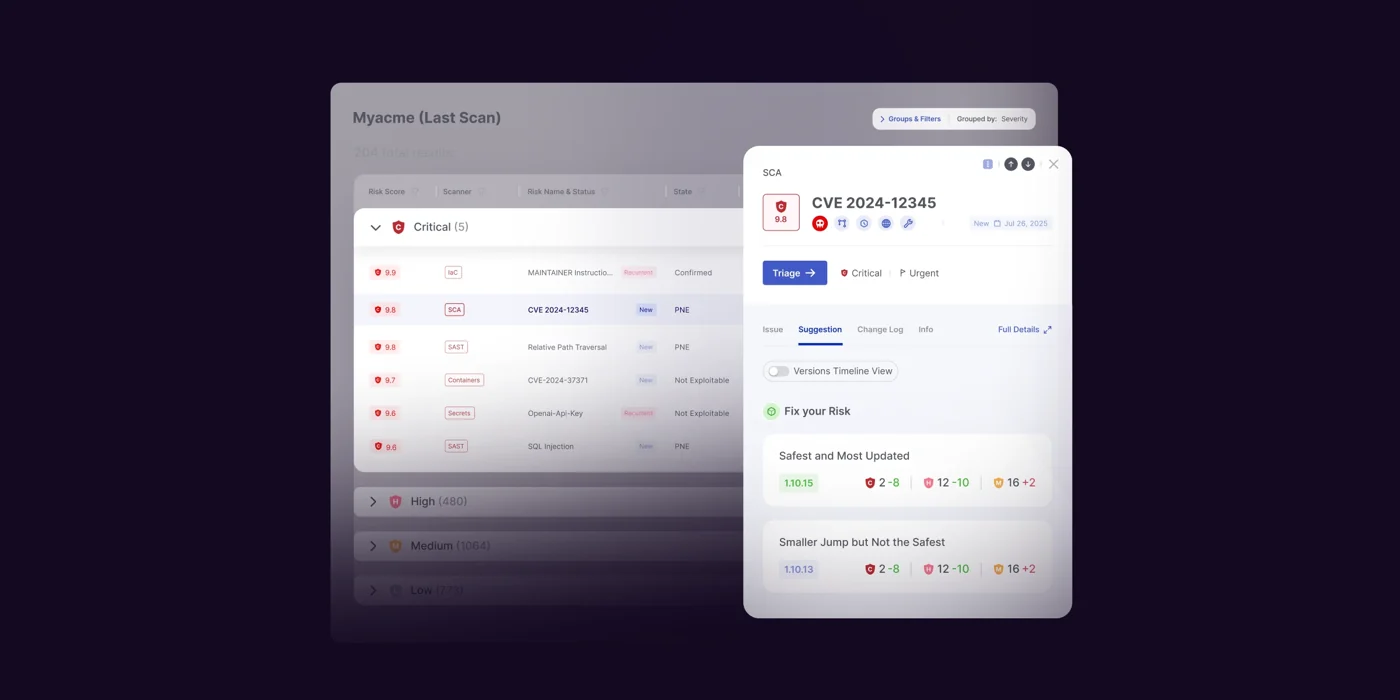
Review open-source dependency assessment.
Review product requirements ↗
Plan application analysis within runtime testing.
Review product requirements ↗
Review application security training for developers.
Review product requirements ↗Checkmarx’s catalogue includes static testing, component analysis, interactive-testing enquiries and Codebashing learning. Static and dependency assessment produce different evidence; interactive testing, where currently supported, depends on exercised runtime paths; learning develops skills rather than assessing a released application. Confirm the current offer and naming for retained catalogue labels before procurement.
Start with languages, frameworks, repositories and application owners. A finding needs context a developer can use, not just a severity. Coverage gaps such as unsupported code, generated artefacts or unexercised paths should remain explicit. A broad platform proposal must identify the actual engines, entitlements and integrations the team will use.
Choose a representative codebase and verify scan prerequisites and narrow access. Trace a known approved issue through triage, assignment, correction and retest. Review direct and transitive dependencies where component analysis is selected. For interactive evaluation, agree instrumentation, workload and potential impact. For learning, review relevant remediation exercises with technical leads.
Code and artefact processing requirements should be approved by the customer before connecting production repositories. UAE organisations may have their own hosting or remote-access constraints. Define risk-based release thresholds and a documented exception route. Handover should leave an application coverage matrix, supported versions, triage ownership and learning follow-up, rather than imply that completion of a course or a green scan proves complete application security.
Useful answers to help you plan your next step.
Discuss your requirements ↗No. Learning supports better decisions and remediation, while the application still needs its agreed assessment and release evidence.
Contact our team about products, installation or ongoing support.
14th Floor, Tamani Arts Building, Business Bay, Dubai
Checkmarx