NSFOCUS Cloud DPS ↗
Plan cloud-delivered DDoS protection coverage.
Review product requirements ↗
DDoS, application and network security platforms. Discuss selection, integration and support requirements with MMC UAE for your Dubai, Abu Dhabi or wider UAE project.
Review individual offerings, then send your requirements for edition, compatibility and service planning.
Plan cloud-delivered DDoS protection coverage.
Review product requirements ↗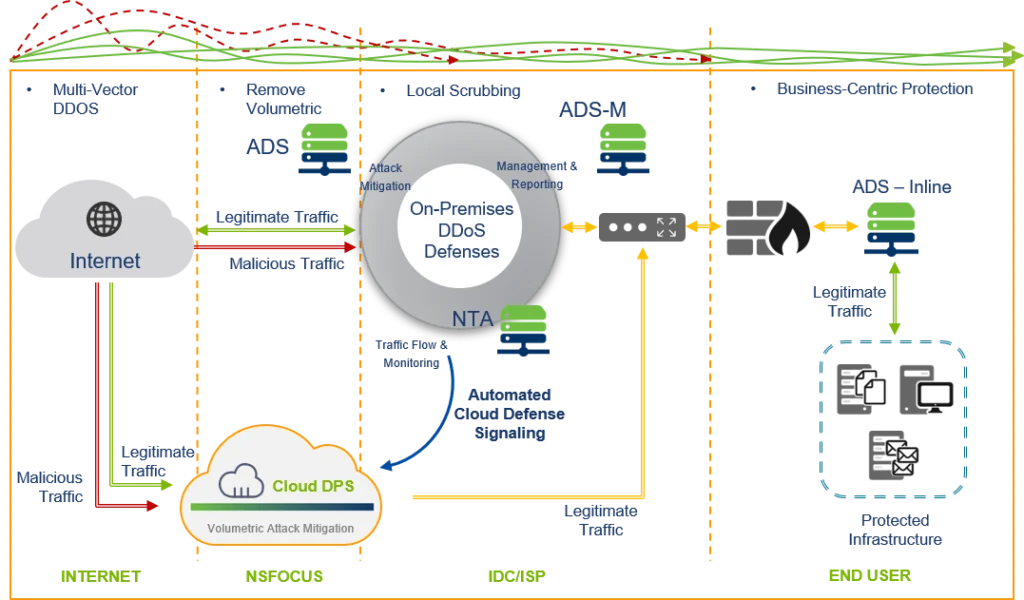
Review DDoS mitigation deployment requirements.
Review product requirements ↗
Plan web application and API traffic inspection.
Review product requirements ↗
Review network policy and firewall migration requirements.
Review product requirements ↗
Plan assessment and vulnerability management workflows.
Review product requirements ↗NSFOCUS’s catalogue includes Cloud DPS, DDoS Attack Protection, WAAP, Next-Generation Firewall and a Threat and Vulnerability Management Platform. Cloud mitigation, site protection, application request handling, network policy and vulnerability assessment serve different parts of the architecture. Begin with the assets, traffic and incidents that need attention.
A DDoS service needs onboarding and an agreed activation or routing design. A firewall migration needs application and network dependencies. WAAP needs legitimate request validation. Vulnerability management needs authorised sources, finding owners and closure evidence. Combining these products should not obscure what is included, how traffic reaches a control or which team responds when a service is disrupted.
Confirm models, interfaces, current subscriptions and supported integrations. Pilot representative traffic and approved assessment cases. For routing or enforcement changes, preserve configuration backups and rollback. Any DDoS validation should use an expressly approved safe procedure rather than uncontrolled traffic generation. For findings, demonstrate applicability review and a retest after an authorised change.
UAE customer requirements should determine processing, remote support and evidence access. Carrier and hosting dependencies need named owners. Handover should include protected scope, activation state, policies, exceptions and escalation. Product capabilities and manufacturer services should remain distinct from MMC implementation or ongoing support commitments; no model name alone establishes a service level or complete protection.
Useful answers to help you plan your next step.
Discuss your requirements ↗No. Validate onboarding, routing or activation and the contracted scope for the actual assets.
Contact our team about products, installation or ongoing support.
14th Floor, Tamani Arts Building, Business Bay, Dubai
NSFOCUS