Group-IB Threat Intelligence ↗
Plan threat intelligence collection and analyst integration.
Review product requirements ↗
Threat intelligence, fraud detection and digital risk protection. Discuss selection, integration and support requirements with MMC UAE for your Dubai, Abu Dhabi or wider UAE project.
Review individual offerings, then send your requirements for edition, compatibility and service planning.
Plan threat intelligence collection and analyst integration.
Review product requirements ↗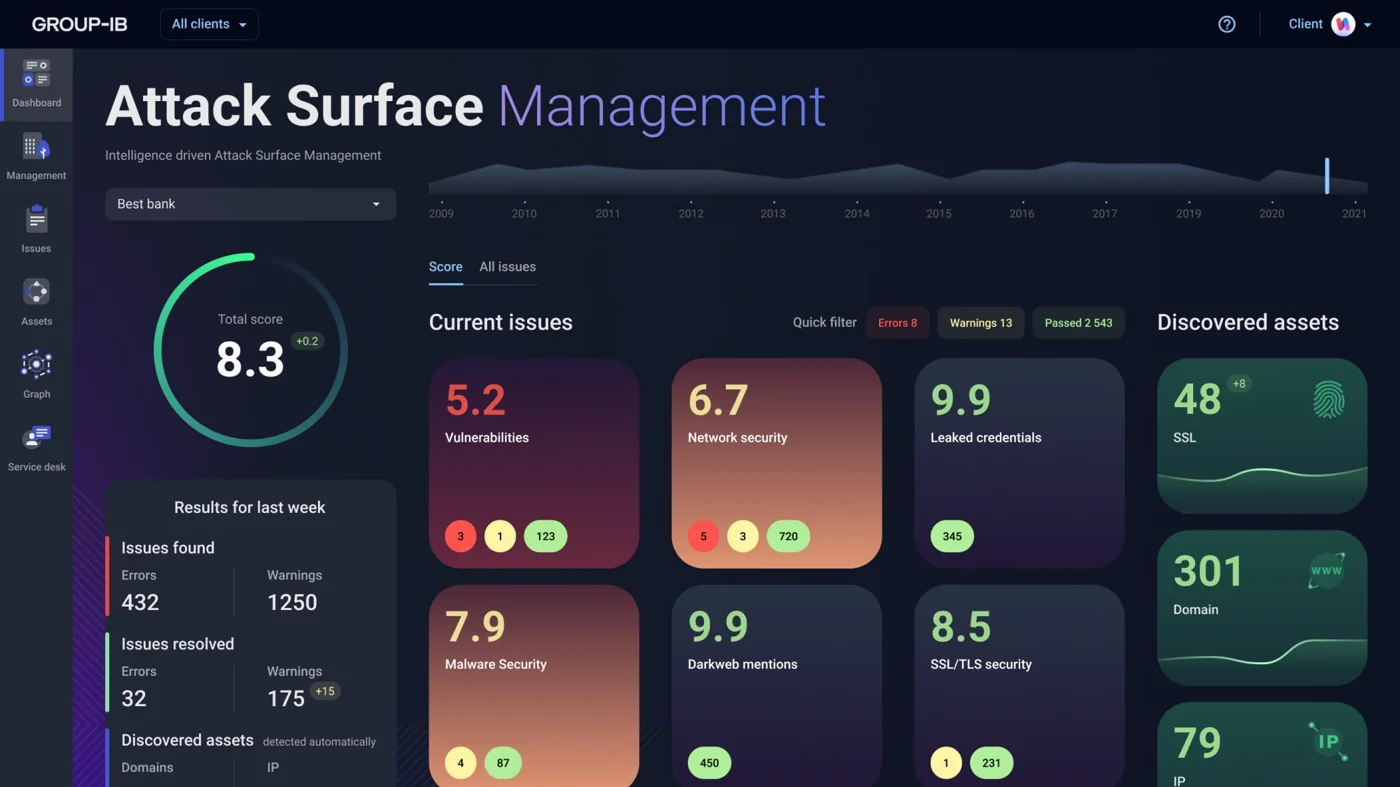
Review discovery and assessment of external assets.
Review product requirements ↗
Plan fraud monitoring around customer-facing transactions.
Review product requirements ↗
Review digital impersonation and external brand risks.
Review product requirements ↗
Plan managed detection coverage and escalation responsibilities.
Review product requirements ↗Group-IB’s portfolio spans Threat Intelligence, Attack Surface Management, Fraud Protection, Digital Risk Protection and Managed XDR. These have different subjects and operational owners. Intelligence informs a decision; external discovery needs asset attribution; fraud work concerns a transaction; brand protection concerns suspected external misuse; managed detection is a service-coverage decision.
Start with the outcome and the authority to act. An external association does not prove asset ownership, a fraud signal is not a final finding about a customer, and an impersonation alert does not itself authorise a takedown. A combined proposal should preserve these distinctions instead of implying one review team can make every decision.
Select representative, authorised examples. Trace an intelligence item into a useful investigation; verify ownership of a discovered asset; review a synthetic fraud case; or follow a suspected brand-abuse item through approval. Confirm supported integrations and the information that must be processed. Include correction of inaccurate attribution or false positives.
For Managed XDR, obtain written sources, hours, response boundaries and customer responsibilities. UAE organisations should identify processing and remote-access requirements before onboarding live evidence. Handover should name the relevant security, fraud, legal or brand owners, with the manufacturer service and any MMC project work separately scoped. No platform output should be converted into a guarantee of removal, prevention or a particular incident outcome.
Useful answers to help you plan your next step.
Discuss your requirements ↗No. Establish ownership and explicit assessment scope before any intrusive activity, even when a discovered association appears plausible.
Contact our team about products, installation or ongoing support.
14th Floor, Tamani Arts Building, Business Bay, Dubai
Group-IB